unicorn.
waking the guardian000

/ cyber security & development

Hi, I'municorn

Cybersecurity student & developer building secure systems and exploring new technologies.

01

About me

I'm a fourth-year Information Security student passionate about cybersecurity, system administration and backend development. I like building things that are reliable, secure and useful.

— unicorn

More about me
3+
Years of study
8+
Certifications
7+
Projects on GitHub
Passion for security

Quick facts

Education

4th year, Information Security

Focus

Security & Development

Location

Chelyabinsk, Russia

Availability

Open to internship

What I work with

Security

  • Pentesting
  • Network Security
  • Threat Analysis
  • Kali Linux

Development

  • Python
  • C++ / C#
  • JavaScript
  • SQL, Flask, FastAPI

Infrastructure

  • Linux, Windows
  • Docker
  • Virtualization
  • VPN

Networks

  • TCP/IP, DNS
  • HTTP / HTTPS
  • Firewalls
  • Proxies
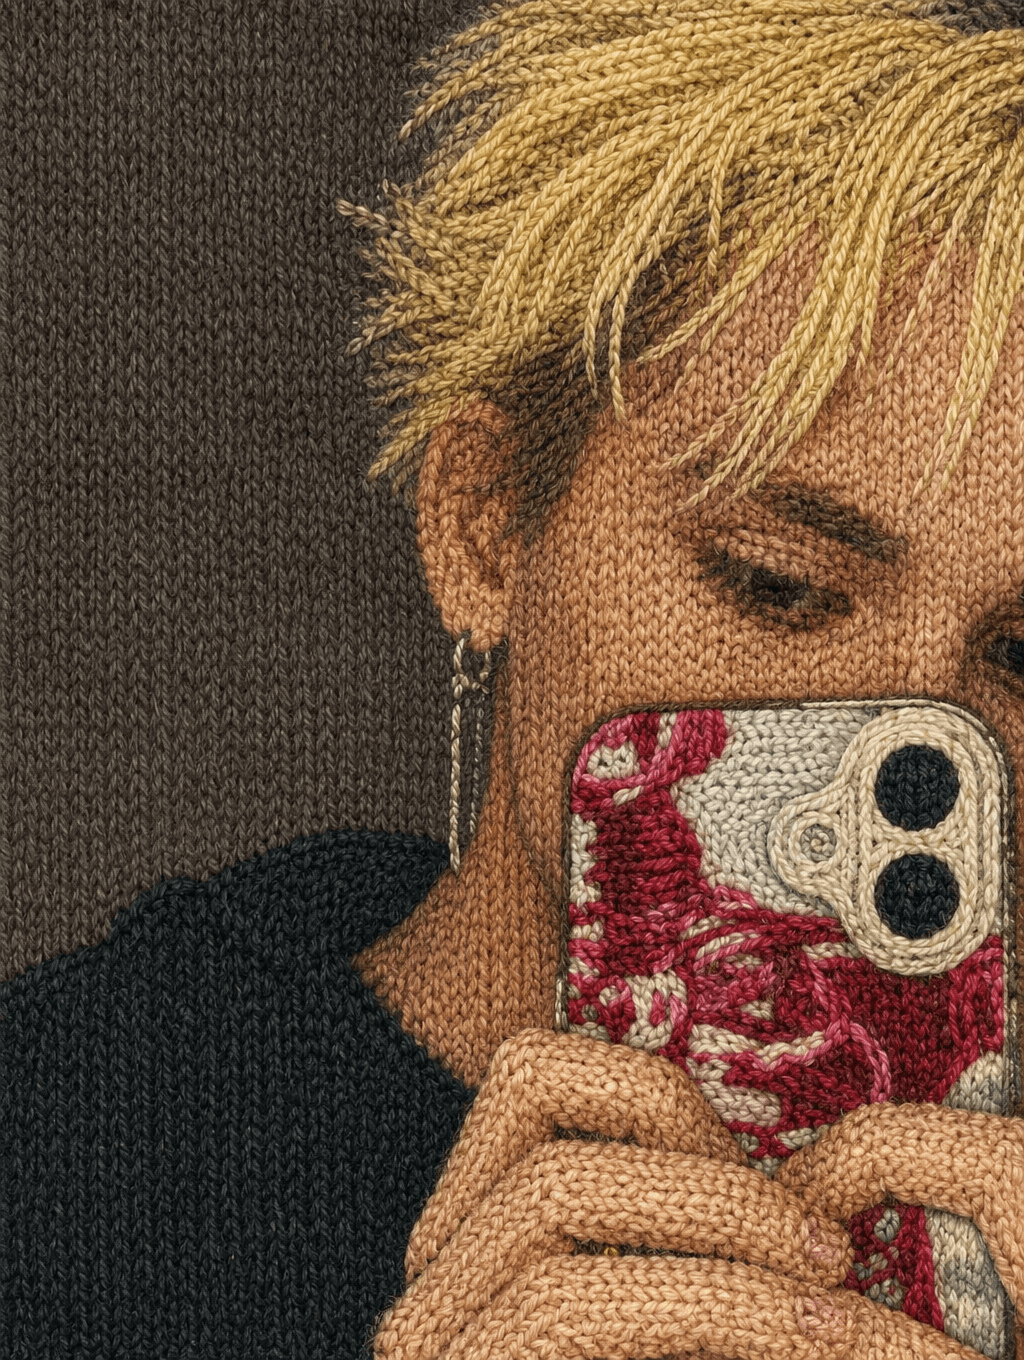
Yaroslav — hand-embroidered portrait
Hand-embroidered portrait
The longer version

A bit more about me

I got into computers early and never really stopped — first taking them apart and fixing them, then writing software, then learning how both of those break. Today I'm a fourth-year Information Security student in Chelyabinsk, and most of my time goes to two things I genuinely run myself.

One half is building. I keep two products in production — an AI platform and a licensed security product — and I own the whole technical side, from the backend and the servers to the desktop client and the release pipeline. The other half is breaking: I audit my own systems, work out how they'd be attacked, and keep the edge sharp on pentest labs and vulnerable machines. I don't think you've really secured something until you've tried to break it yourself.

Along the way I started a small web studio, led a dev team and worked the floor as a club administrator — so I know infrastructure from the terminal and from the moment a real person in front of me just needs it to work. I like making things that are reliable, clear and a little bit hand-made. This whole site — and this portrait — were put together by hand.
02

Skills

What I actually use, grouped the way I think about it. Everything here has been through a real project — a product in production, a test stand or a machine taken apart.

01

Systems and networks

LinuxWindowsTCP/IPDNSHTTP/HTTPSVPN, WireGuard, AmneziaWGnftables, ufwVirtualBox, QEMU/KVMDockersystemdNginxSSH hardening
02

Development

PythonJavaScriptTypeScriptC++ / C#RustSQLReact, Next.jsFastAPI, FlaskTauriPostgreSQL, SQLiteGitBash, PowerShell
03

Security

PentestingWeb application testingNetwork securityAttack analysisThreat modellingCryptographyKali LinuxOSINTHardening and isolationAnti-bot protectionKey and secret handlingBackups and recovery
04

Infrastructure and operations

Server administrationCloudflare: DNS, WAF, TunnelsDeployment and releasesCI on GitHub ActionsMonitoring and alertingIncident responseLog analysis
05

Product and process

Technical documentationThreat modelsLegal perimeter: offer, privacy policyPayments: YooKassaWorking with clients and a teamMentoring
06

Languages

Russian — nativeEnglish — I read documentation freely
03

Toolkit

The tools I reach for, by stage of the work. Five sets, switched like tabs in a terminal — official project marks throughout.

Reconnaissance

nmapmasscanMaltegoSpiderFootenum4linux

Web applications

Burp Suitesqlmapffufgobusterniktodirbwpscan

Passwords and access

hashcatJohn the Ripperhydraimpacketresponder

Network and traffic

Wiresharktcpdumpnetcataircrack-ng

Exploitation and reversing

MetasploitexploitdbSETradare2binwalk
04

Selected work

Two products run in production for real users. The rest are stands and write-ups, built to check solutions by hand rather than by description.

In production

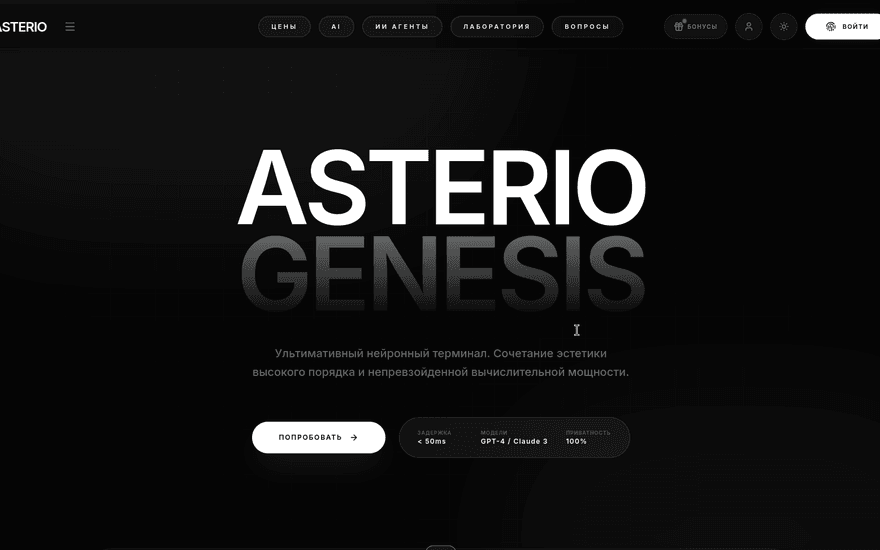
Asterio

2026

AI platform

Co-owner, lead developer and cybersecurity specialist

The first officially registered AI aggregator in Russia. Access to neural networks without a VPN: chat, image and video generation, AI agents, card payments.

ReactTypeScriptFastAPICloudflare
asterio

$ curl -sI https://asterio-ai.com | head -1

HTTP/2 200

# bundle 977 KB → 276 KB after code splitting

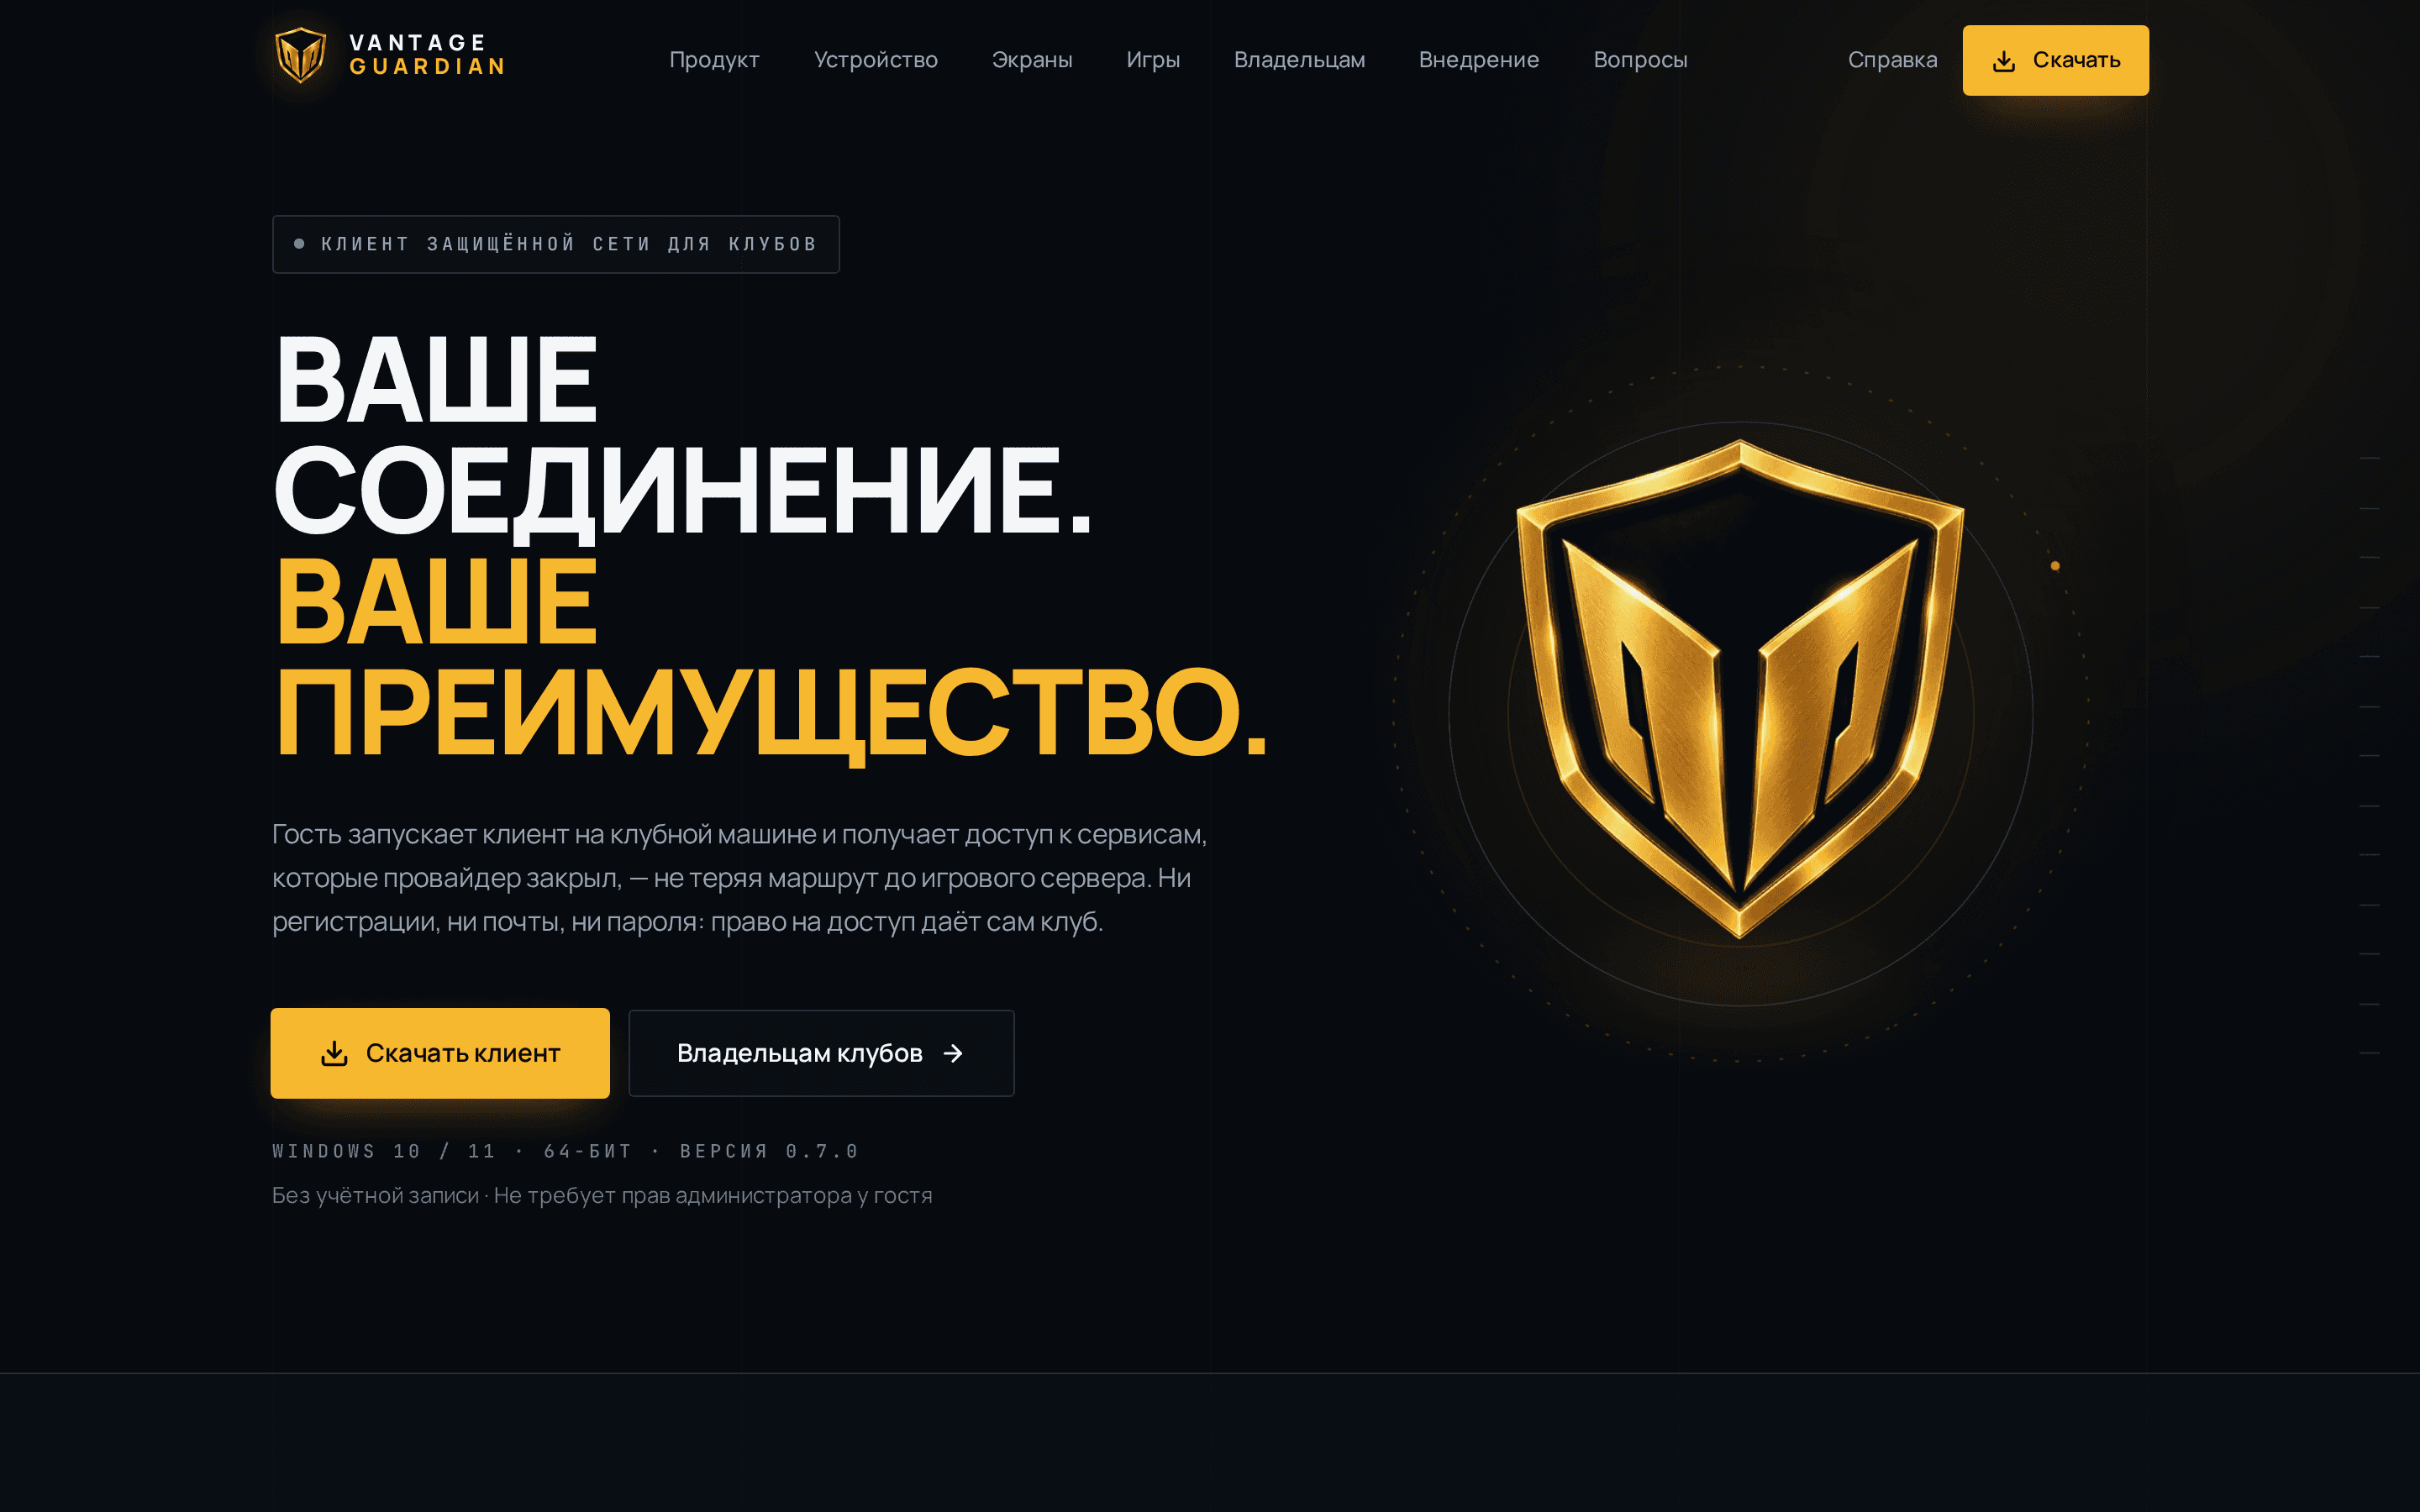
VANTAGE GUARDIAN

2025

Network protection for gaming clubs

Co-owner. Client and server development, security, legal perimeter

The guest presses one button and a tunnel to the game node comes up. The venue's own local networks are never touched.

RustTauriAmneziaWGWindows
vantage

$ vantage status

tunnel up 82 ms 0.0% loss

routes split club network untouched

# a club machine is always treated as untrusted

Stands and research

$ nft list chain inet fw4 forward

oifname != "awg0" counter drop

# nothing leaves outside the tunnel, DNS included

Portable hardened stand

2026

A pocket router nothing leaks past

A pocket router hides all traffic from the attached device in an obfuscated tunnel and lets nothing leak past it. The uplink is a phone over USB; there is deliberately no SIM in the router.

OpenWrtAmneziaWGnftablesCudy TR3000
Read the case

$ Resolve-DnsName example.com -Server 8.8.8.8

timed out

# plain DNS is closed, only DoH remains

win10-hardened-lab

2026

A hardened, isolated Windows 10 in VirtualBox

All DNS is forced through Cloudflare DoH, plain DNS is blocked, host-to-guest channels are closed. Threat model, deployment scripts, isolation checks.

VirtualBoxPowerShellcloudflaredWindows
Read the case

$ nvidia-smi

command not found

# that was the whole root: 1 tok/s → 16 tok/s after the driver

Local LLM agent

2026

The expensive hypothesis was wrong; the cheap check was right

A local model running as an agent in opencode produced 1 token per second. Trying different quantisations changed nothing: the system had no NVIDIA driver and the GPU was computing through Vulkan. After the driver — 16 tokens per second and working tool-calling.

OllamaopencodeCUDAPython
Read the case

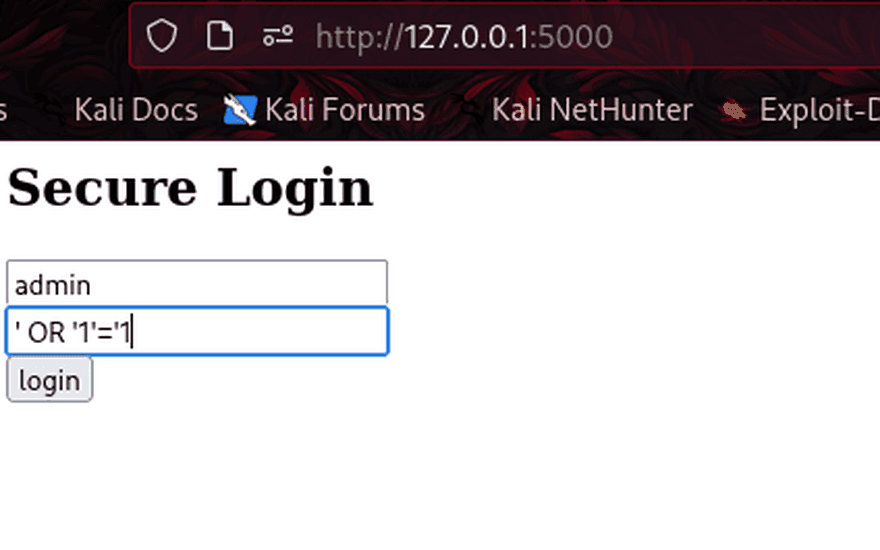
vuln-login

2025

Web pentest training stand

A deliberately vulnerable login form and, in the same folder, the fixed version next to it. You see both the SQL injection itself and what cures it.

PythonFlaskSQLite
Read the case

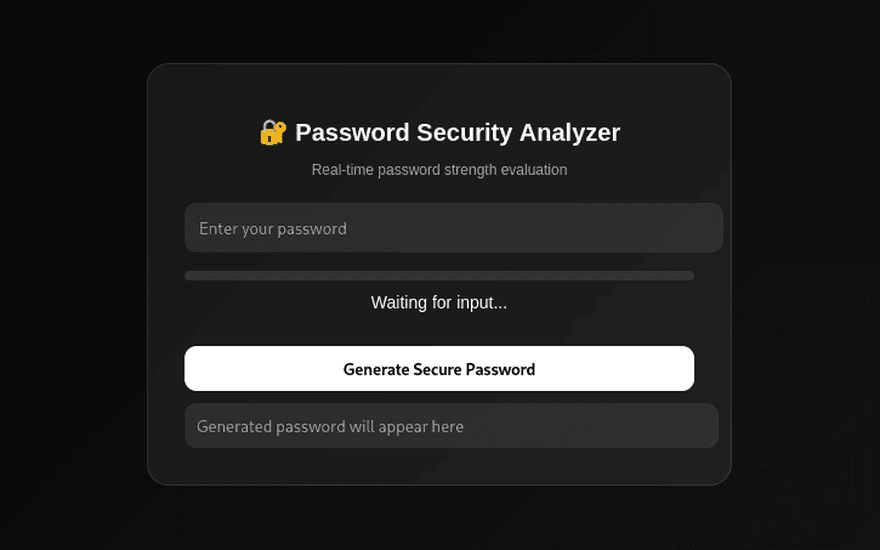
password-tool

2025

Password strength analysis

A scoring model, a check against a dictionary of common passwords, and a generator built on secrets. Web interface, computed on the server.

PythonFlask
Read the case

pentest-lab-writeups

2025

Write-ups from reconnaissance to root

Vulnerable machines taken apart end to end: Mr Robot, Kevgir, Empire LupinOne. Full attack chains with the commands. The stand is nested QEMU/KVM virtualisation on an isolated network.

nmapffufMetasploitJohn
Read the case

Portfolio

2026

This site, built from scratch

The portfolio you're reading. English by default with an instant switch to Russian and no reload, a pre-entry sequence, a hand-cut mascot, one flowing story on Next.js 16.

Next.jsReactTypeScriptTailwindMotionGSAPLenisReact Three Fiber
Read the case
05

Experience

2026 — present

Asterio — co-owner, Backend / DevOps

One of two developers behind the AI platform: I lead the site, the REST API and the server side — FastAPI under Uvicorn in Docker, PostgreSQL behind a connection pool, Redis, Nginx with Let's Encrypt, a three-contour production topology, zero-downtime deploy with rollback. In active development.

2025 — present

VANTAGE GUARDIAN — co-owner · network protection for clubs

Client and server side of a network-protection product for gaming clubs. It runs in the Colizeum club network — that's where the collaboration with Colizeum is now: three clubs, 127 machines, nodes in Frankfurt.

2025 — 2026

Constructa — founder · website studio

My own startup: a small website studio built on one principle — a direct line to the developer, service and unusual projects, run by a close and trusted team. The foundation was ready, but as students with no funding I couldn't carry it then. Good experience and an honest conclusion.

2025 — 2026

Colizeum Cyber Sport Arena — administrator

Ran the club and its machines at a high service bar: client support, diagnostics and repair, workstation setup and optimization. Now in the staff reserve, covering shifts when needed. This is where the trust that turned into the VANTAGE collaboration was earned.

2025

KiberPride — administrator

Ran the floor of a gaming club: guests and bookings, the till and attendance, workstation setup and first-line troubleshooting.

2023 — 2025

BrainFox — lead developer

Led web development for about two years: site architecture and client solutions, requirements gathering, coordinating the team and setting standards, a knowledge base and onboarding.

06

Education

2023 — 2027

Chelyabinsk Radio Engineering College

Comprehensive information security of automated systems. Fourth year now, graduating 2027 — I try to take not only the curriculum but the practice too: solving machines, building stands, reading other people's write-ups.

2025 — 2026

College applied courses

Penetration testing, system administration, information-security basics, Python and C# development, GameDev — the college's hands-on courses alongside the main track.

2025 — present

Self-study

TryHackMe and Hack The Box, red team and blue team. Pentesting pulls me in the most: you see straight away whether the reasoning holds.

2021

TOP Academy — first IT education

Web and app development, Python, C++ and C#, service testing, information security, GameDev and UX/UI design — where the breadth started.

07

Certificates

Verified courses and certifications. Click any one to see the certificate itself.

08

CTF, labs, research

Practise, explore, break, learn. Machines taken apart from reconnaissance to root, on my own stand.

5
machines to root
3
platforms
3
full write-ups
01

Basic Pentesting

TryHackMeMedium

Reconnaissance, SSH brute force with Hydra, cracking an encrypted RSA key in John, privilege escalation through a careless sudo rule (vim from GTFOBins).

nmaphydrajohnenum4linux
Read the write-up
02

Lame

HackTheBoxMedium

Exploiting CVE-2007-2447 in Samba 3.0.20: command injection through username map script gives a root shell straight away, with no escalation step.

nmapmetasploitsmbclientCVE-2007-2447
Read the write-up
03

Mr Robot CTF

TryHackMeMedium

Brute-forcing the WordPress admin password, a PHP reverse shell through the theme editor, root through SUID on nmap in --interactive mode.

wpscanhydraphp-shellSUID
Read the write-up
04

Kevgir

VulnHubMedium

Joomla with CVE-2008-3681, a meterpreter session, escalation through SUID on cp: it is used to overwrite /etc/passwd. The path is www-data to root.

joomscanmetasploitSUID cpCVE-2008-3681
Repository
05

Empire: LupinOne

VulnHubHard

Hidden paths through ffuf, Base58, cracking an SSH key, overwriting webbrowser.py and sudo pip. The path is icex64 to arsene to root.

ffufBase58johnsudo pip
Repository
TryHackMeTryHackMe

Hands-on, one room at a time

Learning offensive security on TryHackMe as @unicorn224. Below are the rooms I've completed and the badges they earned — the theory behind them lives in the encyclopedia.

@unicorn224Rank0x2 · Apprentice7rooms2badge

Completed rooms

Networking

Introductory Networking

The OSI and TCP/IP models, encapsulation, and the first recon commands — ping, traceroute, whois, dig.

Theory
Networking

DNS in Detail

Domain hierarchy, the main record types (A, MX, NS, TXT…) and the full path of a DNS query.

Theory
Networking

HTTP in Detail

Requests and responses, methods, status codes, headers, and how cookies keep a session.

Theory
Linux

Linux Fundamentals Part 1

The terminal: moving around, reading files, searching, and chaining commands with operators.

Theory
Windows

Windows Fundamentals 1

How Windows is built inside: NTFS and ACLs, System32, account types and SYSTEM, UAC.

Theory
Tools & recon

Offensive Security Intro

A first taste of offensive security — content discovery and directory brute-forcing on a target.

Theory
Foundations

Defensive Security Intro

The blue-team side: prevention vs detection & response, the areas of defence (SOC, threat intel, DFIR, malware analysis, SIEM), and a SOC analyst repelling an attack.

Theory
AnthropicAnthropicAcademy

How AI actually works

The other side of my learning — courses from Anthropic, the makers of Claude, on how generative models really behave. Where TryHackMe is hands-on hacking, this track is understanding the machine. Every course earns a verified badge.

In focus

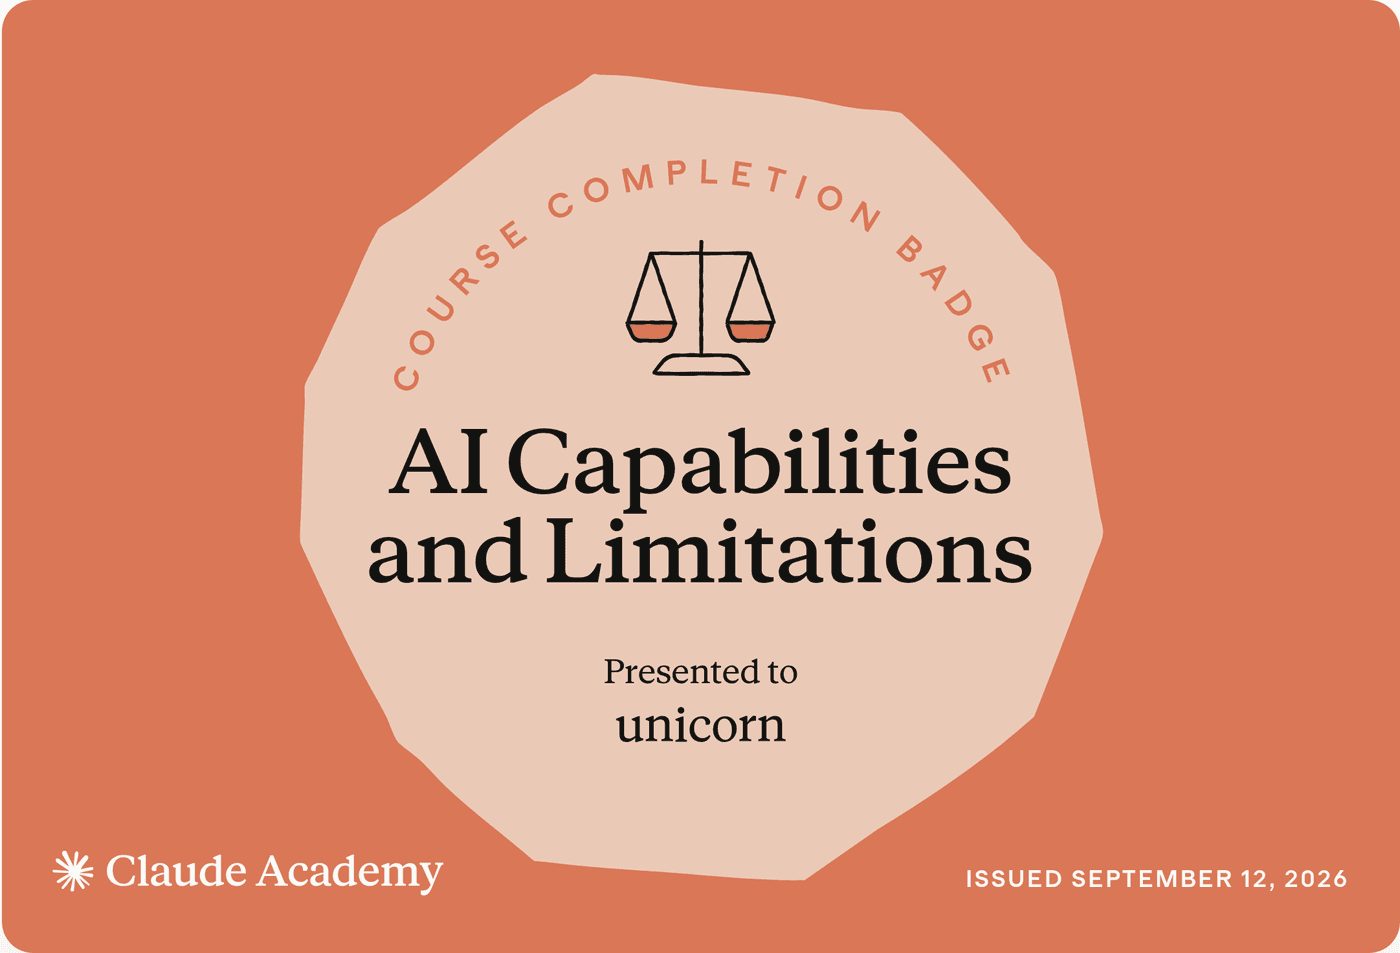
AI Capabilities and Limitations

13 lessons·~3.5h·completed Sep 2026

A working mental model of how generative AI behaves and why — so an unexpected answer reads as a known kind of error with a precise fix, not a mystery.

Verify badge
AI Capabilities and Limitations

The mental model it gives you

Four properties explain almost any behaviour of a generative model — name the one that slipped, and the fix is obvious.

Next-token prediction

fluent ≠ correct

Answers are built one token at a time as a plausible continuation, not looked up from a fact store.

Knowledge

confidently wrong

Knowledge is baked into the weights with a training cut-off; without tools there's no live world — hence hallucinations.

Working memory

the edge of the window

The context window is all it holds right now. In a long chat the early parts fall off the edge.

Steerability

guided, not guaranteed

Instructions steer the output strongly but never guarantee it — conflicts and a safety priority set the limits.

Completed courses

09

Companies

Places where I gained experience and made an impact.

Colizeum2025 — 2026

Colizeum

A chain of gaming clubs

Administrator, now in the staff reserve; and the network-protection client (VANTAGE) runs in their venues.

Constructa2025 — 2026

Constructa

A website development startup

Development and markup, SEO, working with clients.

KiberPride2025

KiberPride

A gaming club

Running the floor, maintaining machines and consoles.

BrainFox2023 — 2025

BrainFox

A small web studio

Markup and website development, animation, SEO.

Rostelecom2022 — 2023

Rostelecom

A large internet provider

Working with networks and subscribers, support.

Open to work

Looking for an internship
or a junior role

A fourth-year information-security student already running two products in production. I want a place where I can apply what I know, be useful to a team and grow under people stronger than me. Areas that interest me most:

Get in touchFull-time · on-site, hybrid or remote · Chelyabinsk

Cybersecurity

Pentesting, network security, threat modelling, hardening and isolation — checked by hand on my own stands and machines.

AI & backend

Working with LLMs and agents, and the server side around them: FastAPI, PostgreSQL, Redis, queues, payment and legal perimeters — the way Asterio is built.

Infrastructure & DevOps

Linux, Docker, Nginx, Cloudflare, CI, zero-downtime deploy, monitoring and incident response. Servers that stay up under load.

Networks & VPN

Tunnels and obfuscation (WireGuard, AmneziaWG), split routing, DNS, firewalls — from the VANTAGE client and the TR3000 stand.